IT Infrastructure
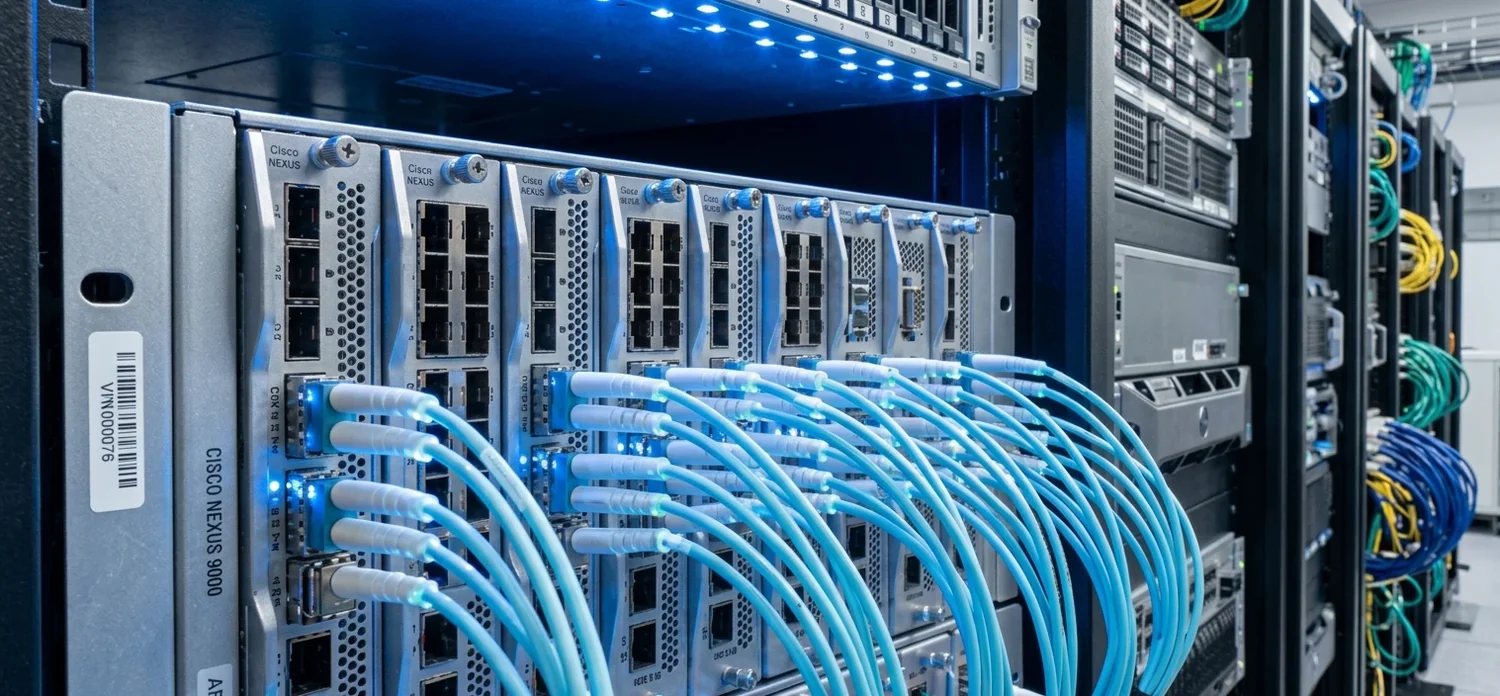
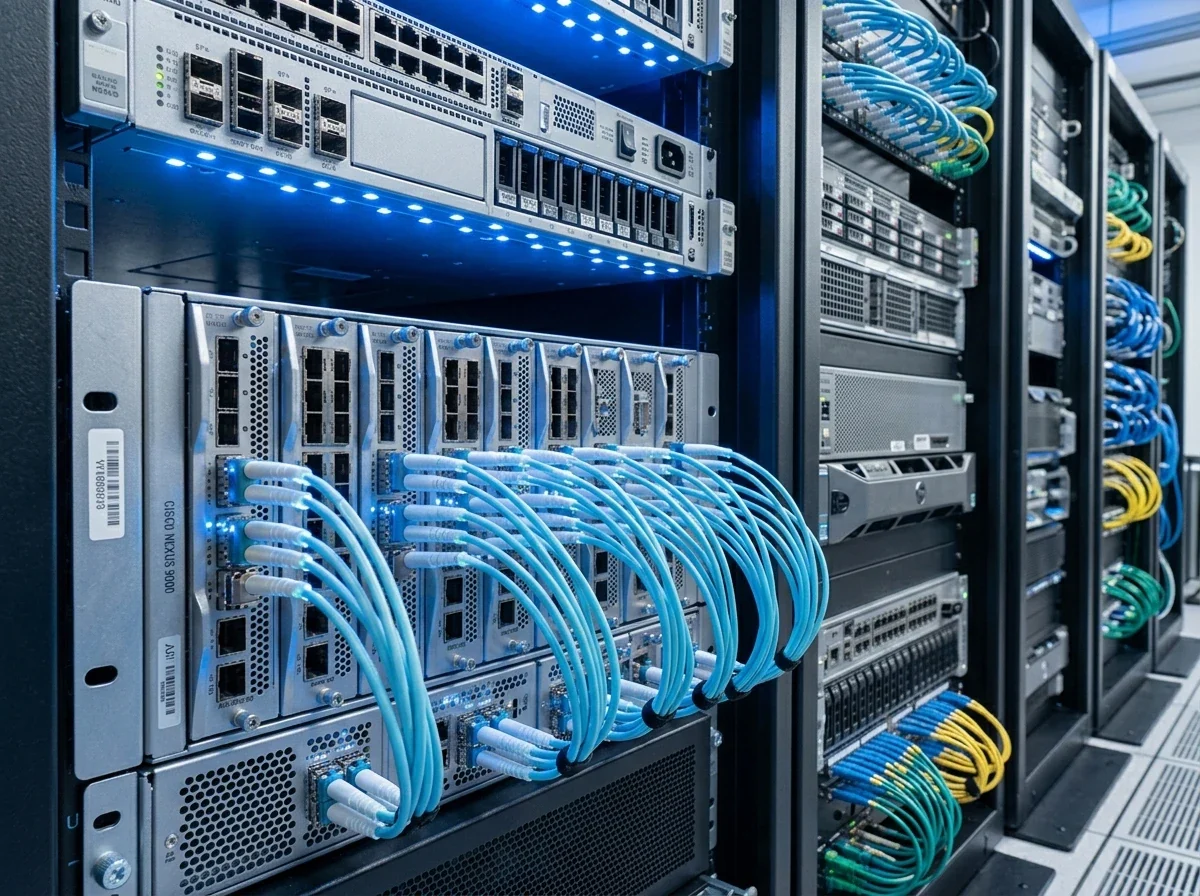
High-density server configurations, virtualization clusters, SAN/NAS storage arrays, and deterministic computing stacks engineered for maximum fault tolerance.
- Bare-Metal Systems
- Hyperconverged HCI
- Tier III/IV Spec
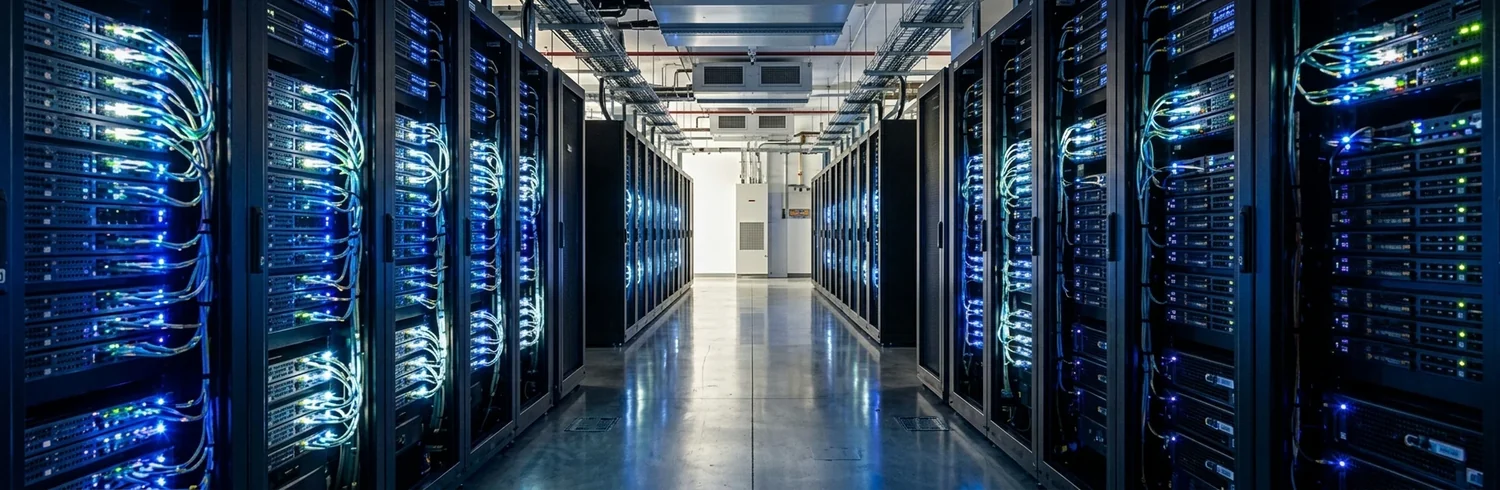
Networks, servers and cloud environments designed as one estate — specified for fault tolerance, watched around the clock, and built to carry what your business runs on.
Infrastructure, engineered
Modern digital enterprises cannot thrive on fractured systems. We synthesize enterprise on-premise hardware, high-throughput SD-WAN fabrics, and multi-cloud environments into a singular, highly predictable ecosystem designed for maximum fault tolerance.
Every switch port, routing table, and cloud compute cluster is specified with mathematical rigor. We eliminate single points of failure while continuously lowering systemic latency across distributed physical and virtual assets.
Explore Our InfrastructureOur core capabilities
From core IT systems to cloud architecture, we design and manage the technology that keeps your business connected.
High-density server configurations, virtualization clusters, SAN/NAS storage arrays, and deterministic computing stacks engineered for maximum fault tolerance.
Multi-gigabit SD-WAN, zero-packet-drop core switching, BGP routing, and low-latency fiber transport architectures.
Multi-cloud orchestration (AWS, Azure, GCP), hybrid edge configurations, microservices container orchestration, and dynamic auto-scaling.
Layered zero-trust frameworks, automated threat detection, cryptographic key rotators, identity enforcement, and continuous audits.
Immutable cold storage, automated failover pipelines, instant snapshot restoration, and continuous compliance verification.
Deterministic real-time operations console featuring micro-latency tracking, predictive hardware fault diagnostics, and 24/7/365 command response.
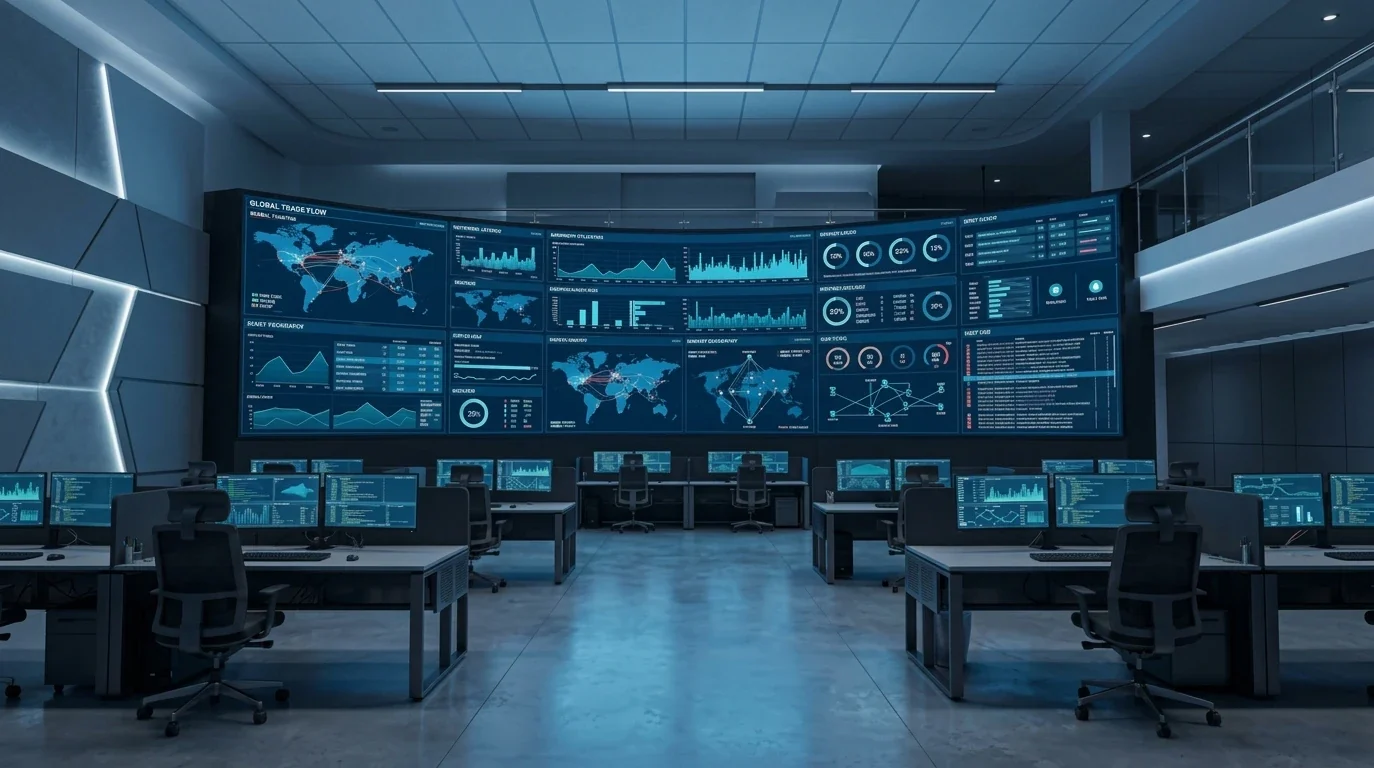
End-to-end flow architecture
A deterministic pipeline connecting edge nodes, campus branch offices, and distributed hyperscaler databases.
Hybrid scalability
Deterministic lift-and-shift or phased re-architecture without service interruption. Rigorous pre-flight latency mapping and synchronized database cutovers.
Infrastructure-as-Code (Terraform, Pulumi) deploying declarative, version-controlled topologies across hybrid environments with embedded zero-trust boundaries.
FinOps algorithmic telemetry, continuous resource right-sizing, reserved instance scheduling, and automated egress cost containment.
Defense-in-depth
Eliminate perimeter vulnerability with non-bypassable, hardware-attested cryptographic controls.
Role-based adaptive MFA, contextual passwordless SAML tokens, and real-time device posture validation.
Micro-segmented VLANs, line-rate IPsec hardware crypto, automated TLS 1.3 termination, and DDoS absorption.
Mutual TLS between microservices, dynamic rate-limiting, and deep packet heuristic payload inspection.
FIPS 140-2 Level 3 HSM key isolation, automatic field-level encryption, and immutable air-gapped snapshots.
Continuous CSPM drift remediation, least-privilege IAM continuous scanning, and multi-cloud perimeter lockdowns.
Automated SIEM event correlation, AI-augmented anomaly detection, and rapid automated kill-switch scripts.
Engineered for performance
From micro-second optical switching in Tier-4 colocation cages to globally distributed VPC clusters, every byte travels through predictable, enterprise-grade conduits.
Methodology
A disciplined, five-phase deployment lifecycle that mitigates operational risk and guarantees zero unanticipated disruption.
Full audit of hardware, bandwidth utilization, topology paths, and software dependencies.
Engineering high-availability blueprinted diagrams, packet flows, and budget models.
Parallel stage provisioning, automated validation scripts, and canary routing.
Penetration testing, RBAC identity binding, and zero-trust verification certificates.
Continuous latency telemetry analysis, dynamic caching, and capacity auto-scaling.
Infrastructure dynamically designed for compounding enterprise compute demands.
Uncompromising defense-in-depth protection engineered directly across every network layer.
Deterministic low-latency routing architecture ensuring uninterrupted global operations.
Automated disaster recovery and multi-region failover built intrinsically into the blueprint.
Begin architectural consultation
Speak directly with a Principal Infrastructure Architect. Receive an exhaustive audit of your network latency, cloud spending, and threat exposure within 5 business days.
SOC 2 Type II certified · ISO 27001 compliant · 99.999% SLA backed